+5.7k
Covert Channels
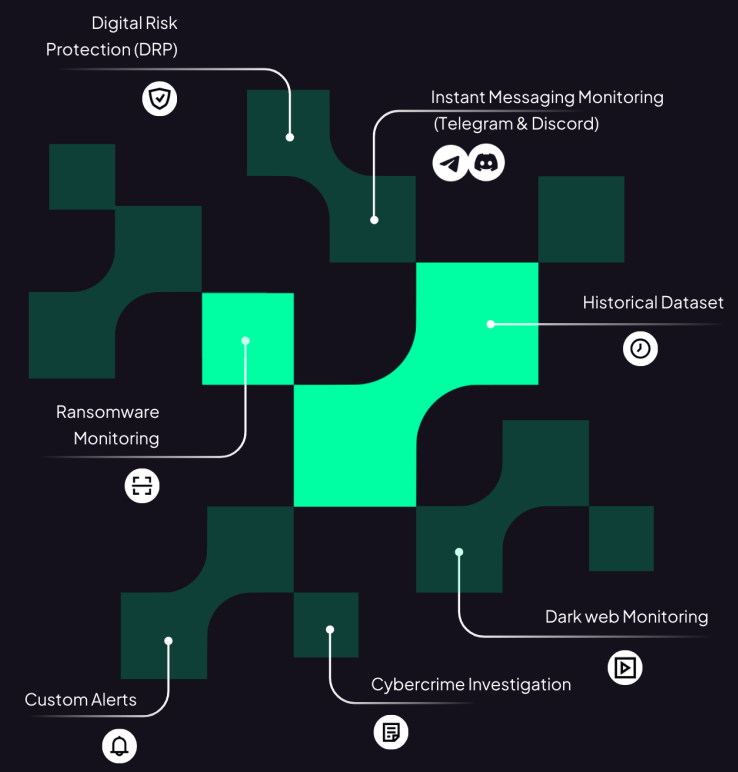
Real-time indexing across Telegram, Discord, and +600 darkweb forums to intercept threat actors.
Most threat intelligence leaves security teams drowning in darkweb noise. Byron Labs combines scientific rigor with automated monitoring to deliver high-fidelity, validated intelligence—so you can anticipate threats, not just react to them.
Discover Vysion PlatformDeep underground coverage and seamless interoperability designed for high-velocity SOC teams.
Real-time indexing across Telegram, Discord, and +600 darkweb forums to intercept threat actors.
Tracking +220 ransomware groups and +23k attacks to neutralize threats before intrusion.
Daily unstructured signals ingested directly into API and MISP feeds to power your SOC without noise.
We don't stay on the surface. Vysion monitors the hardest-to-access sources where attackers coordinate their operations: Darknet (Tor/I2P), encrypted messaging (Telegram/Discord), and restricted Initial Access Broker (IAB) forums.
Combining academic research heritage, high-category government compliance, and industry-leading technology partnerships.
Explore our most in-demand capabilities—where human analytical expertise and scientific rigor address your most critical security challenges.
Research-led attack simulations combining AI automation with live Vysion dark web leaked credentials, and active exploit payloads.
Learn moreBreach containment, memory forensics, and root-cause analysis executed directly by senior security engineers.
Learn moreOn-demand intelligence reports, threat actor attribution, VIP Auditing and targeted threat research.
Learn moreArchitecture hardening, automated SIEM/SOAR deployment aligned with CIS benchmarks and NIS2 standards.
Learn more"The best team of information security experts in Spain, and one of the best in Europe and the world, brought together within a highly trusted scale-up."
— Pablo García Mexía, PhD. | Head of Digital Law at Herbert Smith Freehills Kramer Spain
The same analysts protecting your infrastructure are constantly investigating the global cybercrime landscape. Explore the latest open insights, tactical threat analysis, and deep-dive intelligence reports developed entirely by the Byron Labs Cyber Intelligence Team.