


Native MISP Module & Feed:
Compatibility: MISP 2.4+ with MISP Modules and Python 3.8+. Setup: enable vysion-expansion and add the Vysion feed in the MISP UI.
Enrich MISP events with darknet intelligence and ransomware victim data.
Vysion's native MISP module enriches emails, domains, URLs, phone numbers, and crypto wallets with darknet and ransomware context, while a dedicated feed brings new ransomware victims into MISP. Explore the integration below and see how it fits your sharing workflows.
Discover VysionThe Vysion expansion module and ransomware feed bring direct, transparent intelligence from darknet networks, clandestine messaging platforms, and ransomware archives into MISP without hidden scoring algorithms or network filters.
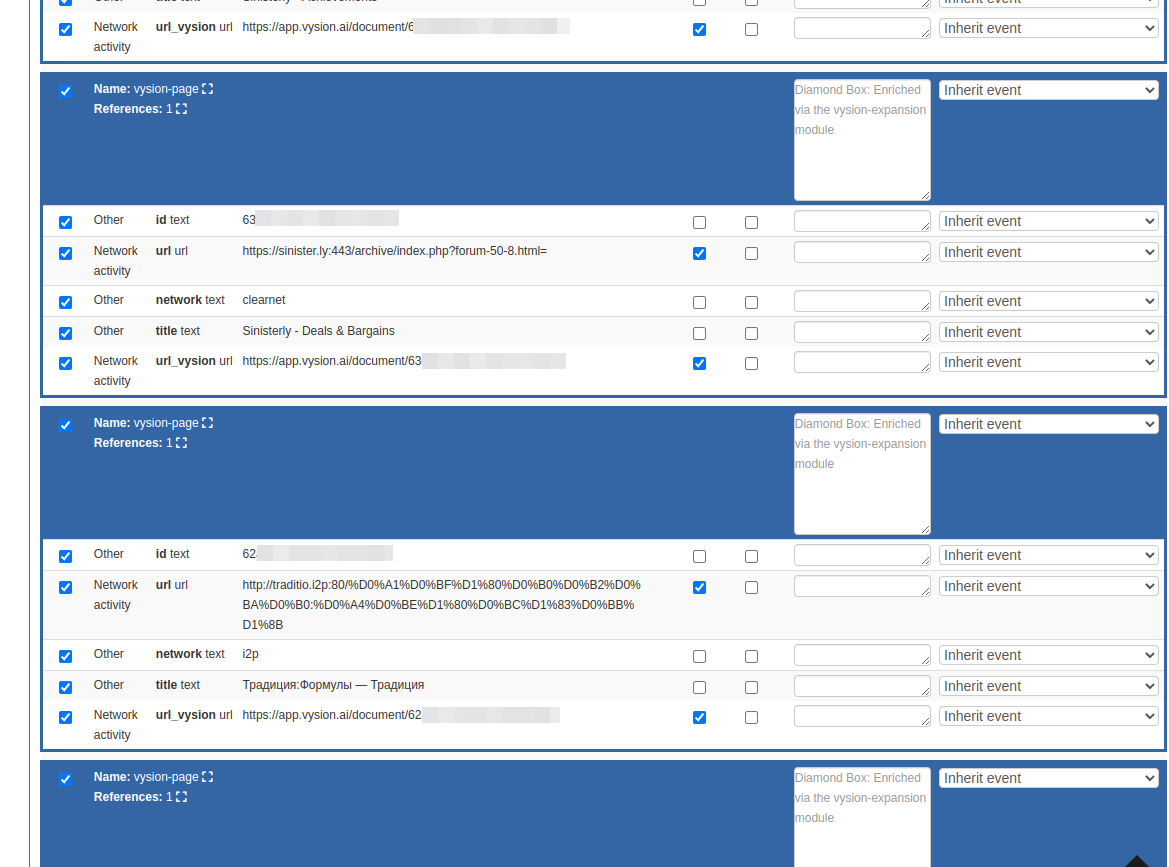
Unfiltered indexing across Tor (.onion) and deep web networks, returned as vysion-page objects with title, URL, content, detection date, and tags.
Victim records delivered as vysion-ransomware-feed objects: company name, ransomware group, leak site URL, website, industry, country, and description.
Search BTC, XMR, and DASH wallet attributes directly from MISP to reveal where they appear across underground sources.
Engineered for CTI analysts, SOC teams, and CERTs to enrich, correlate, and share underground intelligence—delivering evidence-backed context directly inside MISP events.
Right-click any supported attribute and run the Vysion expansion to add vysion-page objects and related attributes.
Fetch newly identified ransomware victims, leak site URLs and sector data as a native MISP feed.
Add dated darknet and ransomware findings to MISP events to support timelines and investigation context.
Install the Vysion module with the automated installer, manually, or via Ansible, then add your Vysion API key in MISP plugin settings.
View Integration GuideCompatibility: MISP 2.4+ with MISP Modules and Python 3.8+. Setup: enable vysion-expansion and add the Vysion feed in the MISP UI.
Connect your enterprise Vysion API Key for high-throughput, unlimited enrichment across all supported attribute types.
Turn underground intelligence into shared, actionable context across four high-impact operational scenarios—from incident triage to community sharing.
Speed up triage by enriching suspicious emails, domains, URLs, and phone numbers already in your MISP events. Vysion reveals where they surface across darknet forums adding evidence-backed objects with detection dates and source URLs.
Stay ahead of extortion campaigns with a continuous feed of newly identified victims. Each record includes ransomware group, leak site URL, industry, and country, ready to correlate with your sector, clients, and suppliers.
Follow the money behind cybercrime. Pivot from BTC, XMR, and DASH wallet attributes to the darknet pages and conversations where they appear, and connect them to the actors and ransomware operations in your events.
Share Vysion-enriched events with trust groups, ISACs, and CERT communities using MISP's distribution controls, and export indicators to your IDS and SIEM through MISP's native formats.
Install the Vysion module in your MISP instance and add your API key to enrich attributes and import ransomware victims with darknet context.